
What was reported
Microsoft introduced a cloud web applications threat matrix aligned with MITRE ATT&CK. It connects risks across application code, managed runtimes, identities, deployment pipelines, and associated cloud resources.
Source: Microsoft Security Research · 9 September 2026The club take
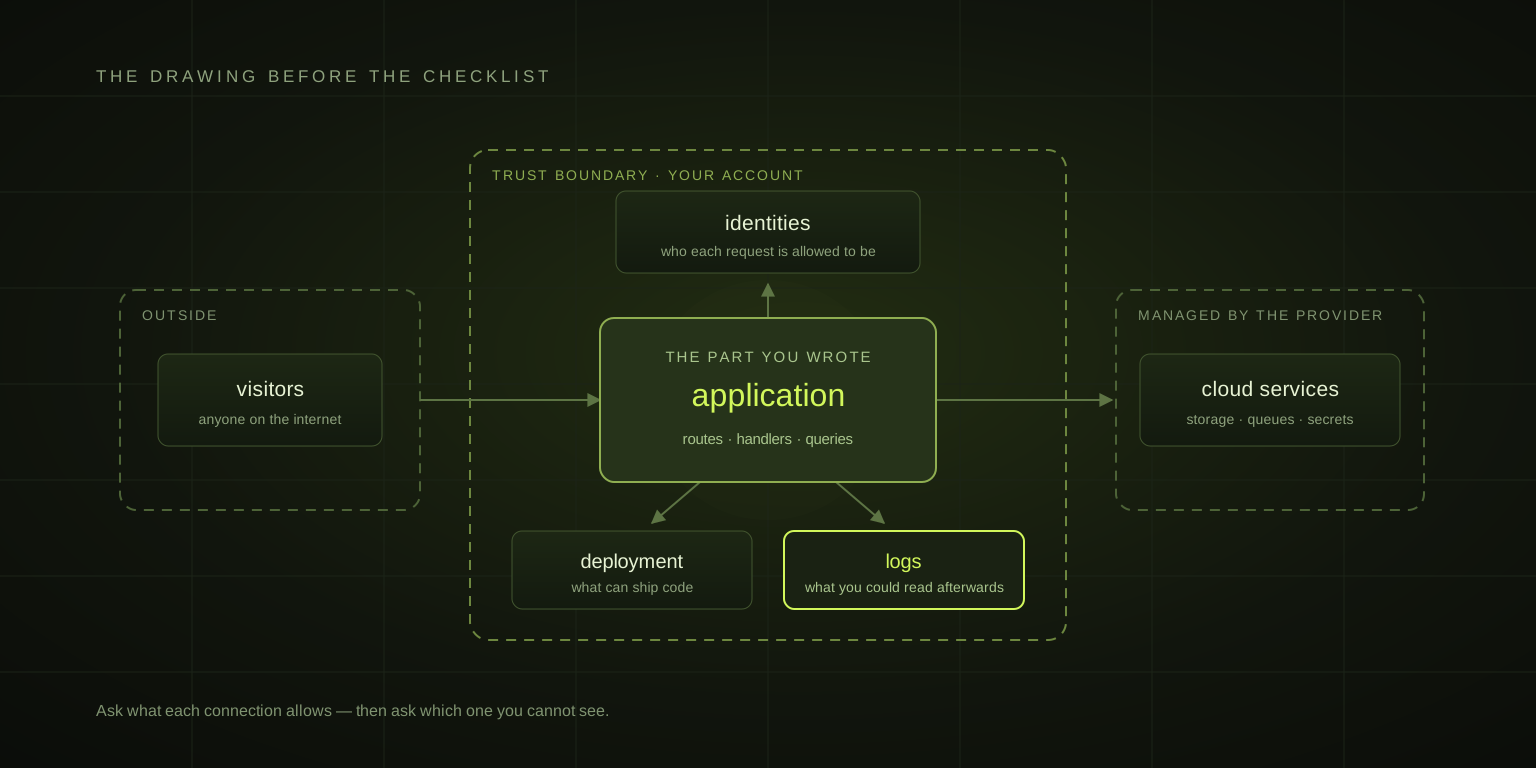
OUR INTERPRETATION & WORKSHOP IDEASOur takeaway: a small architecture drawing can be a better first security conversation than a long checklist. Start with the app, then add the identities, deployment path, and services it relies on. Ask what each connection allows.
For a collaborative lab, choose an intentionally simple demo and mark its trust boundaries together. One person explains the application, another follows the deployment process, and a third asks which logs would help investigate an unexpected action. Treat the published matrix as a discussion aid, not a claim that every listed risk exists in your project.